Uncompromised: The New Blueprint for Product & Third-Party Defense
Agenda
3:00–3:05 PM | Welcome & Introductions
Setting the stage for the next generation of product and third-party cybersecurity.
3:05–3:45 PM | Executive Panel Discussion
An interactive conversation exploring threat modeling, third-party dependencies, modern attack vectors, and the leadership decisions required to strengthen cyber resilience.
3:45–4:00 PM | Audience Q&A
Your opportunity to engage directly with the panelists.
Who you will hear from.
Kevin Fu is a professor at Northeastern University with appointments in Electrical and Computer Engineering, the Khoury College of Computer Sciences, and Bioengineering. He previously served as Acting Director of Medical Device Cybersecurity at the FDA’s Center for Devices and Radiological Health and as Program Director for Cybersecurity in the FDA’s Digital Health Center of Excellence.
He earned his PhD from MIT and is a Sloan Research Fellow and Fellow of IEEE, ACM, and AAAS. MIT Technology Review named him a TR35 Innovator of the Year.
A seasoned cybersecurity executive with extensive experience leading global security programs in healthcare and enterprise environments. Formerly Global CISO at Stryker, where he helped the organization navigate a disruptive cyberattack and before that he held a CISO position at Siemens Healthineers. With over two decades of experience spanning defense, telecommunications, Retail, and healthcare, David specializes in building and managing security operations centers (SOCs), threat intelligence programs, and incident response teams. He is the author of Designing and Building Security Operations Centers and a recognized thought leader in operationalizing cybersecurity at scale. David's work focuses on advancing patient safety by aligning cutting-edge cyber defense with the unique demands of healthcare environments, ensuring resilience against evolving global threats.
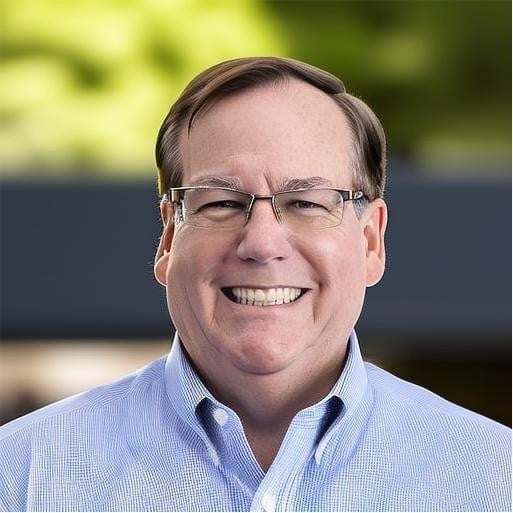
Ed Gaudet is Founder and CEO of Censinet, a healthcare cybersecurity company pioneering collaborative enterprise and third-party risk management through its cloud-based platform and exchange. With more than 30 years of experience in enterprise software, SaaS, cybersecurity, and governance, risk, and compliance (GRC), Ed has built and scaled innovative technology companies, contributing to two IPOs and multiple acquisitions. A member of the Forbes Technology Council, he is focused on transforming how healthcare organizations identify, assess, and manage vendor risk to strengthen cybersecurity, operational resilience, and patient safety.
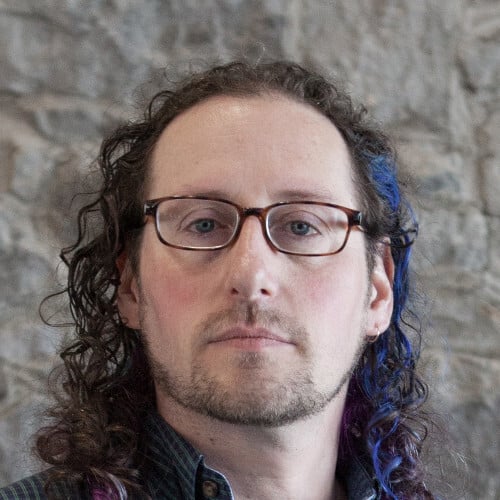
Adam Shostack is President of Shostack & Associates and a leading expert in threat modeling, secure-by-design principles, and cybersecurity innovation. He helped create the Common Vulnerabilities and Exposures (CVE) system and played a key role in advancing Microsoft's Security Development Lifecycle, developing tools and techniques to identify security risks early in software design. An Affiliate Professor at the University of Washington, Adam is the author of Threats: What Every Engineer Should Learn from Star Wars and Threat Modeling: Designing for Security. His career spans Microsoft and multiple successful cybersecurity startups, with a focus on making security more effective, practical, and accessible.